· adswds-team · Security · 3 min read
PHP out-of-memory can become unauthenticated RCE: CVE-2026-109618
PHP advisory, 21 Oct 2026: CVE-2026-109618 (CVSS 4.0 9.2) lets OOM interrupt a half-initialized request. Unauthenticated RCE is demonstrated on mod_php. Fixed in 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
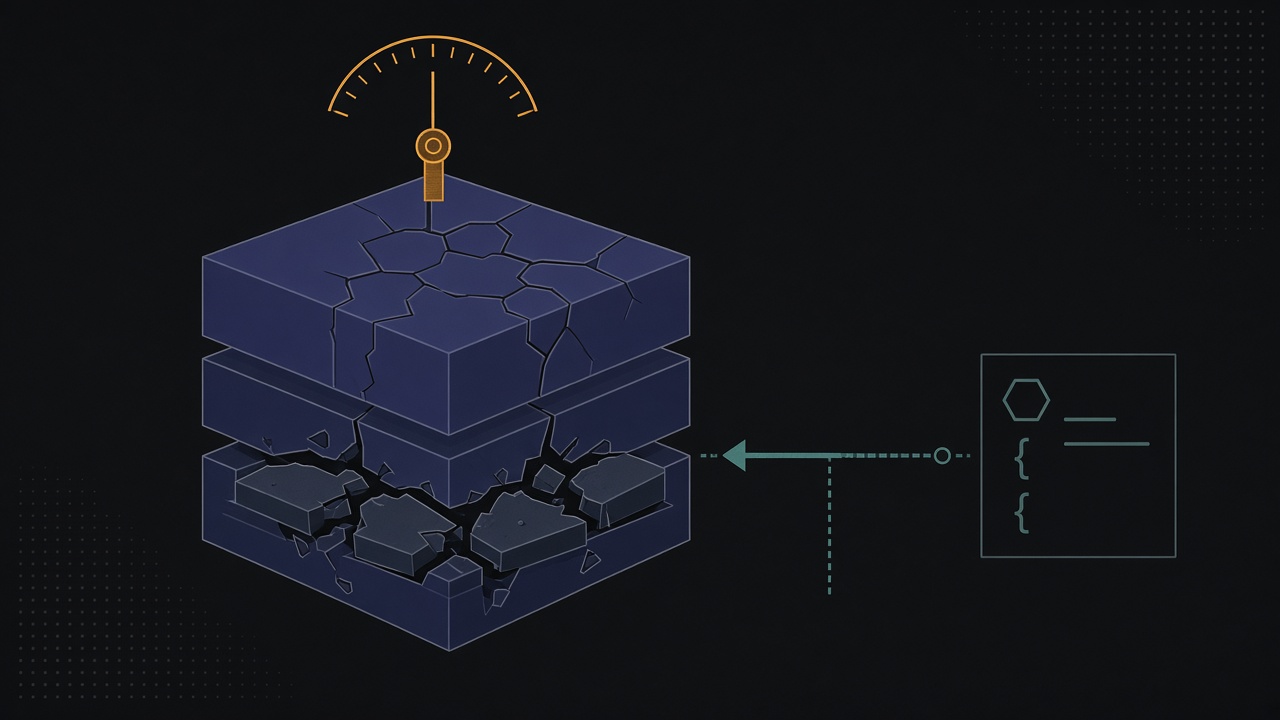
The PHP security advisory (21 Oct 2026) and GHSA-w8hw-w9fx-j79w describe CVE-2026-109618: on out-of-memory, PHP uses longjmp() to leave the current context. If that happens while request memory is only partly initialized, request shutdown can treat the invalid state as valid. The advisory says every install serving web requests is in scope—PHP-FPM, Apache mod_php, php-cgi, FrankenPHP, and LiteSpeed—with the highest risk on mod_php, where an unauthenticated request can trigger the issue before any application code runs.
In one line: the landing page’s PHP may be reached before your script is.
The same release fixes the separate CVE-2026-109619. Configuration workarounds do not stand in for each other.
What is confirmed
| Item | Detail |
|---|---|
| IDs | CVE-2026-109618 / GHSA-w8hw-w9fx-j79w |
| Severity | Critical, CVSS 4.0 9.2 (AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H) |
| Affected | Branch builds before 8.2.35, 8.3.36, 8.4.27, 8.5.12 |
| Fixed | 8.2.35, 8.3.36, 8.4.27, 8.5.12 |
| Confirmed impact | Unauthenticated RCE as the web worker account |
| Validated | HTTP RCE against mod_php with default input and memory limits, normal prefork, multiple workers |
| FPM | Source analysis says it can still be susceptible; no complete FPM exploit has been demonstrated for this issue. A failed request startup exits the child |
| FrankenPHP | Calls request shutdown unconditionally, so the advisory treats application-independent attacks as likely |
| LSAPI | Modelled on FPM; application-specific exploitation is called likely but unvalidated |
The oss-security note from the PHP security team matches the advisory: the failing allocation need not be the invalid memory itself. The UK NCSC has asked operators to act on both CVEs. AWS bulletin 2026-143 lists affected ranges as 8.5.0–8.5.11, 8.4.0–8.4.26, 8.3.0–8.3.35, and 8.2.0–8.2.34.
The advisory also describes multipart parsing paths that can exhaust memory while still looking inside post_max_size. This post does not repeat those constructions. The operational point is that a small body cap on the proxy does not, by itself, prove the PHP memory limit held.
Versions
- Move each active branch to its fixed release above.
- PHP 8.1 and older no longer get routine updates from the PHP project. The advisory says the security team shipped minimal source backports for 7.4, 8.0, and 8.1 for people building from source without a vendor LTS. Ask the distribution about packages.
- PHP 8.2 reaches end of life on 31 Dec 2026 (8.2.35 announcement).
- The volunteer repo
rpms.remirepo.netwas not going to have packages on announcement day. Use distribution packages or a source build.
The patch stops using longjmp() for OOM. It switches to a delayed soft OOM at the next VM safe point, and a hard _exit() at a second, higher threshold.
If you cannot upgrade today
The advisory is explicit: updating is the only complete fix.
- Set
memory_limit=-1withphp_admin_value(FPM pool or Apache) and check that no pool, directory, or app puts a finite limit back. An underlyingmmap()failure can still hit the old path. - Without uploads,
post_max_size = 8M. With uploads,post_max_size = 32Mand keepupload_max_filesizebelow it. - Cap decoded body size, field count, multipart parts, headers, and nesting at the server or proxy, including requests without a usable Content-Length.
- A cgroup
memory.maxcan bound availability if it kills only the worker. Do not useRLIMIT_ASorRLIMIT_DATA. - Apply the CVE-2026-109619 guidance as well.
Landing-page hosts
If the landing page runs on your own PHP host, the exposed runtime is that PHP, not the HTML. The usual pack target is PHP 8.3, so the fixed build is 8.3.36. On mod_php the failure is before application code, so “we don’t call dangerous functions” is not a control.
Visitor rules do not catch a runtime fault while the request body is still being parsed. Upgrade the interpreter, then tune rules.
Summary
CVE-2026-109618 is the 21 Oct 2026 PHP RCE with a demonstrated unauthenticated mod_php path. Fixed releases are 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Schedule hosts, not individual sites.
Sources: PHP news archive, GHSA-w8hw-w9fx-j79w, oss-security, NCSC.